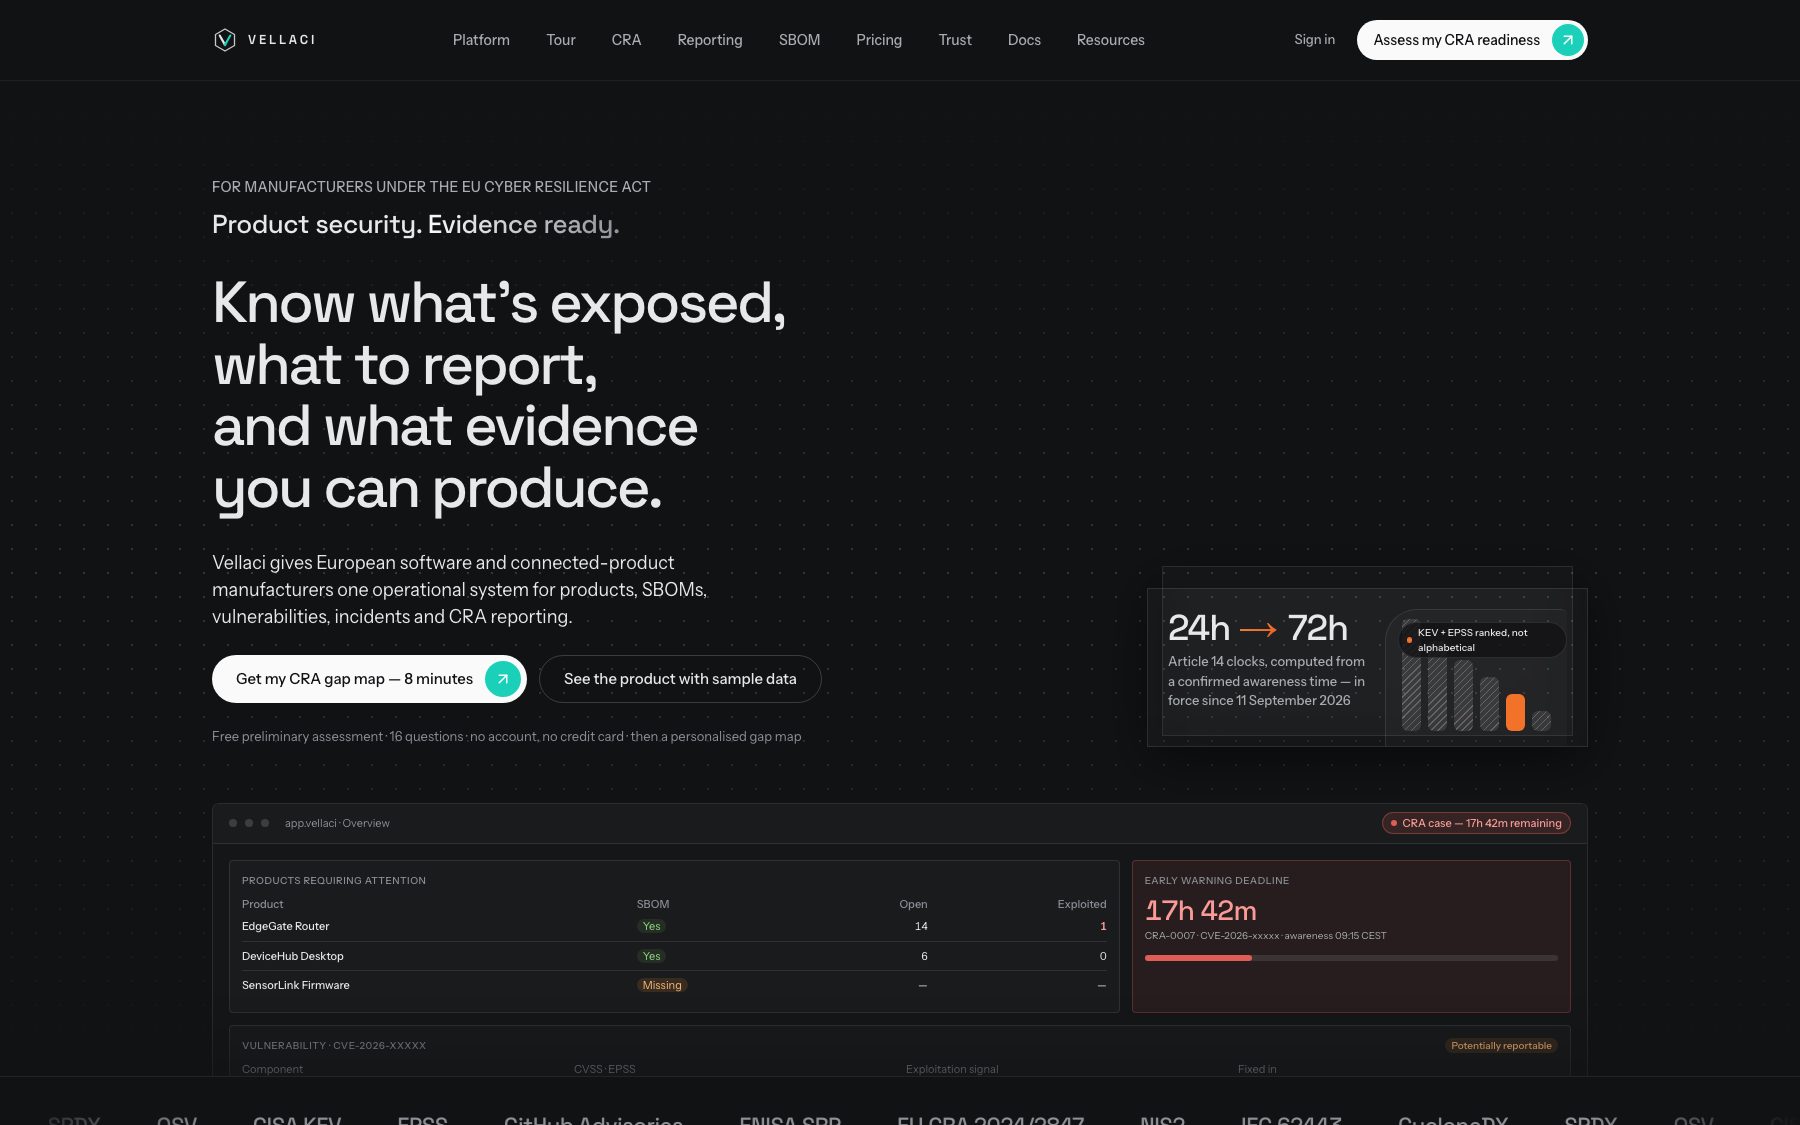
Vellaci offre ai fabbricanti europei di software e prodotti connessi un unico sistema operativo per prodotti, SBOM, vulnerabilità, incidenti e reporting CRA. Ogni versione supportata ha il suo SBOM; ogni componente viene confrontato in continuo con OSV, gli advisory GitHub, CISA KEV ed EPSS. Quando un revisore nominato conferma che un evento è segnalabile ai sensi dell’Articolo 14, gli orologi delle 24 ore, delle 72 ore e del rapporto finale partono da quella decisione — e ogni salvataggio finisce in un registro di audit concatenato per hash e in un caveau di prove con checksum.
Leggi il caso studio completo in inglese →
Il prodotto come sistema
- Product + SBOM
- Vulnerability match
- Reviewer decision
- Article 14 clocks
- Submission + evidence
Cosa è stato consegnato
- SBOM ingestion (CycloneDX, SPDX) with continuous matching against OSV, GitHub advisories, CISA KEV and EPSS — exposure becomes a query, not a project
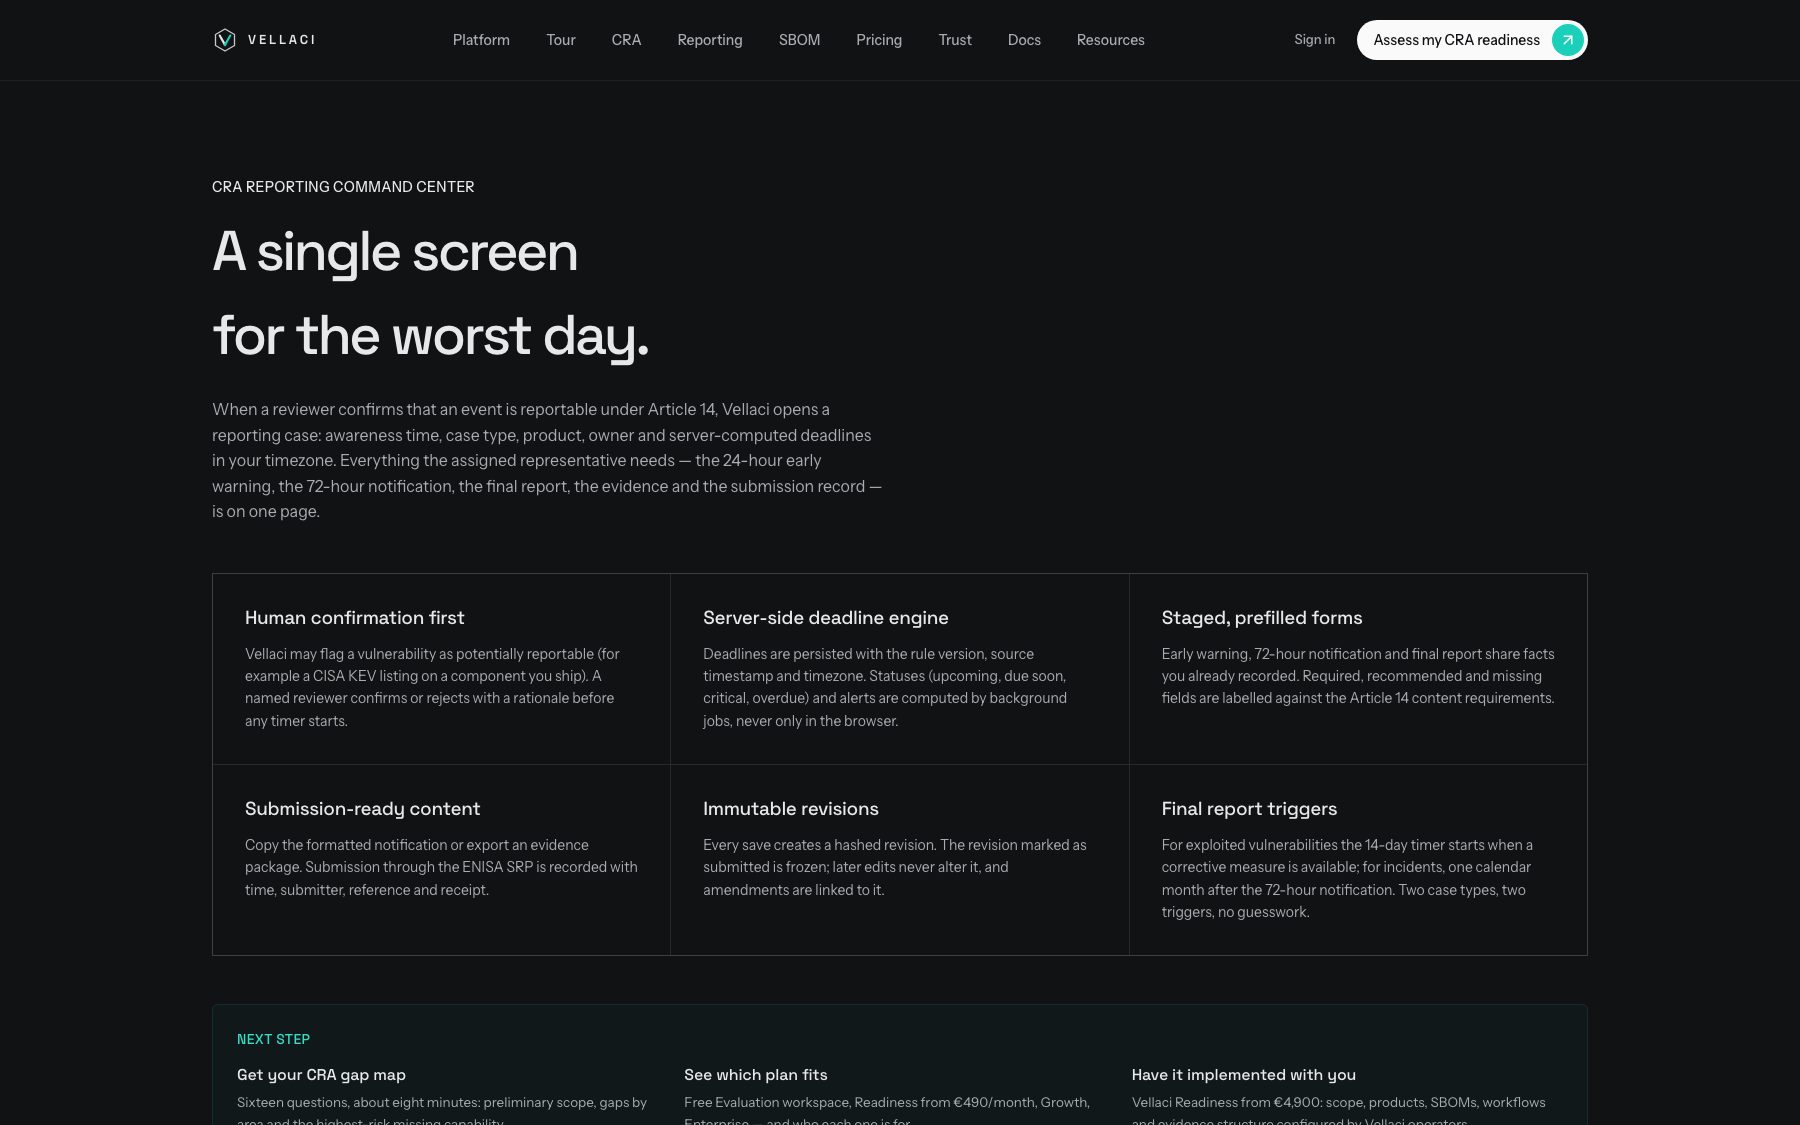
- Article 14 clocks computed server-side from a confirmed awareness time, with the rule version, source timestamp and timezone persisted; statuses and alerts run as background jobs
- Human confirmation before any timer: a named reviewer confirms or rejects reportability with a rationale, so the deadline has an owner and a defensible start
- Immutable revisions — every save is a hashed revision, the submitted one is frozen, amendments link back to it — plus a checksummed evidence vault exportable at any time
- Vulnerabilities ranked by exploitation signal (KEV + EPSS), not alphabetically
- A free 16-question readiness assessment as the top of the funnel: the gap map is shown before an e-mail address is asked for
Schermate
Capacità dimostrate qui
Il servizio corrispondente
- SaaS developer — A complete SaaS product — auth, roles, data, payments, admin, deployment — built for its first real customer.
- Custom web application — Internal tools, client portals, eligibility engines, back offices — the software that replaces the spreadsheet and the emails.
- Architecture and product audit — The paid diagnostic before the build: v1 scope, target architecture, risks, plan and budget. CHF 2’400, seven working days, 100% credited against the build.
Per approfondire
- Next.js architecture for a production SaaS: the decisions I make on every productWhat separates a Next.js project that holds from one that gets rewritten after a year comes down to about ten decisions. Here are mine, as applied on Atamatax, Horvera, Wabiro, SponsorsMetrics — and on this site.Next.js & full-stack9 minLeggi →
- Prototype or v1: the difference that decides your launchA prototype impresses in a demo. A v1 survives the first real customer. Confusing them is expensive.Costruire prodotti5 minLeggi →
Sistema successivo
SponsorsMetrics