B2BProduct security
EU Cyber Resilience Act compliance for product manufacturers
In production · subscriptions live
- Problem
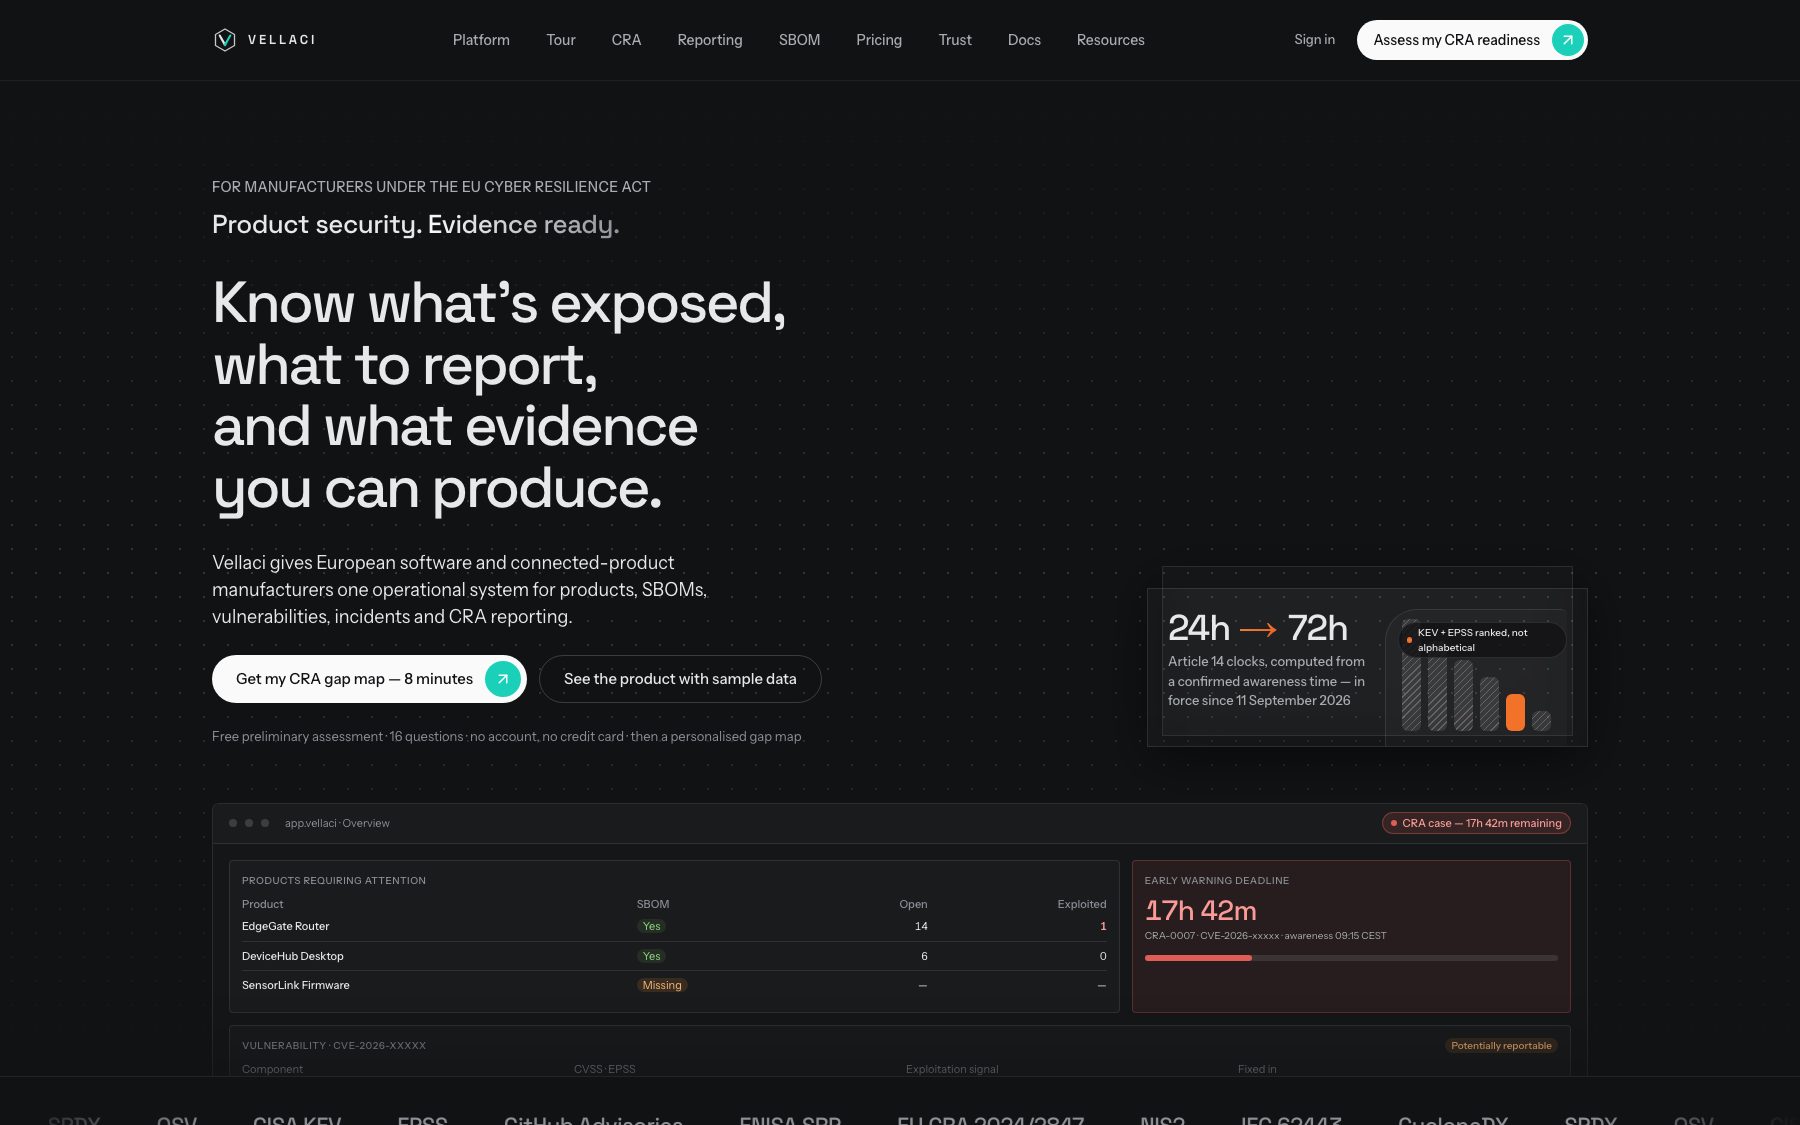
- The EU Cyber Resilience Act turns product security into questions with legal deadlines — what is exposed, what must be reported inside 24 and 72 hours, what evidence can be produced — and most manufacturers answer them from spreadsheets and ticket timestamps.
- System
- SBOM ingestion · vulnerability intelligence · deadline engine · evidence vault
- Role
- Research, product, regulatory modelling, engineering, payments, search acquisition
- Hardest part
- A reporting clock a regulator will accept: it starts when a named reviewer confirms awareness with a rationale — not when a ticket was created — and it is computed server-side with its rule version, source timestamp and timezone persisted, never only in the browser.